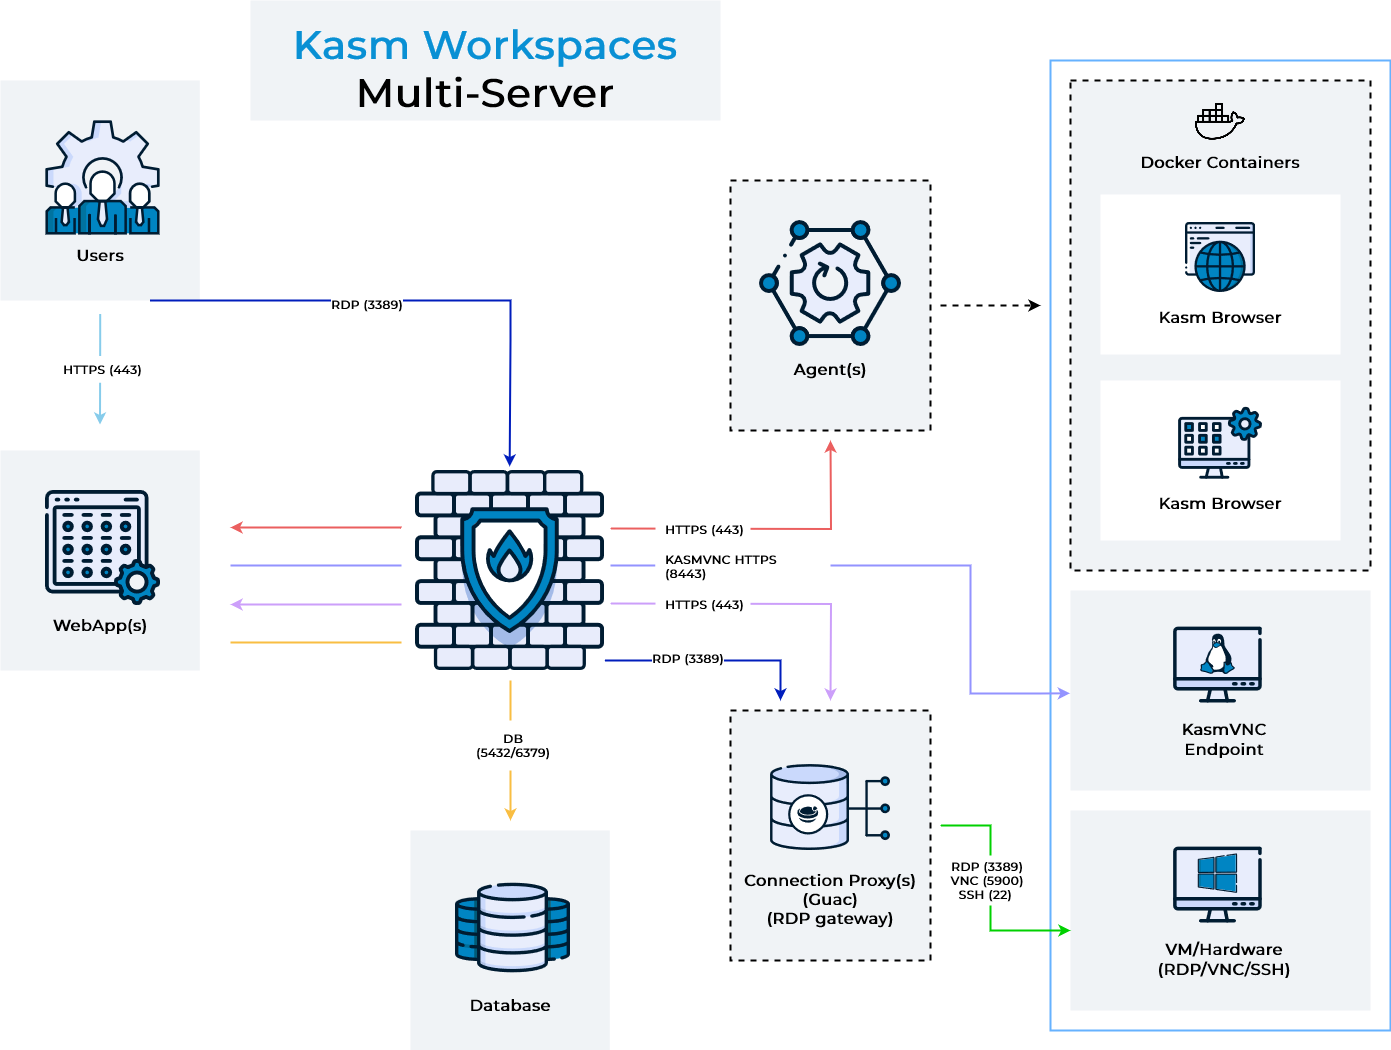
Architecture Roles
The following outlines the Role Service in this architecture. The ports and protocols required for communication are listed to allow for firewalls or filtering devices in your environment
Web App Server(s)
This is the landing point for end users. If end-users access this server from the internet this may be put in a DMZ enclave. This Server includes the following services:
- Web Application (kasm_api)
- Manager Service (kasm_manager)
- Proxy (kasm_proxy)
- OTel Collector (kasm_otel_collector)
- Ports / Protocols
- HTTPS (443)
Database Server
The database server must be accessible by API and Management Services. This Server includes the following services:
- Database Service (kasm_db)
- Ports / Protocols
- POSTGRESQL (5432)
Agent Server(s)
Agents are where end-user sessions are created. Depending on the desired architecture these may be placed in various locations. The agent must be accessible by the Management and Web App Servers. This server includes the following services:
- Ports / Protocols
- HTTPS (443)
ClickHouse (Observability Database) Server
The ClickHouse observability database stores all telemetry (logs, traces, and metrics). In a multi-server deployment it runs on its own dedicated server and must be accessible by the Web App Server, which reads telemetry for the UI reports and log viewer and forwards telemetry to it through the OTel Collector. This is a required role for a multi-server deployment, exactly like the Database Server. ClickHouse is bundled on the node only in a single-server (
all) installation. This server includes the following services:
- ClickHouse Service (kasm_clickhouse)
- Ports / Protocols
- HTTPS (8443) — secure ClickHouse HTTP interface, used by the Kasm API for UI reports and the log viewer
- Secure Native TCP (9440) — secure ClickHouse native interface, used by the OTel Collector to write telemetry
This role does not run an OTel Collector and does not forward telemetry on its own; it is a storage endpoint only.
Both ports are published to the network over TLS so that the app/all node can reach it.
For details, see the Observability configuration reference page.
Connection Proxy(s)
Connection proxies are used to broker web native RDP/VNC/SSH and RDP thick client sessions to fixed or autoscaled servers. If this functionality is not needed, this role does not need to be installed. Connection proxies need to be accessible from the WebApp servers and to the destination RDP/VNC/SSH servers. If RDP thick client access is desired then the Connection Proxy role must be internet accessible. This server includes the following services:
- Guac Service (kasm_guac)
- RDP Gateway Service (kasm_rdp_gateway)
- proxy (kasm_proxy)
- OTel Collector (kasm_otel_collector)
- Ports / Protocols
- HTTPS (443)
- RDP (3389)